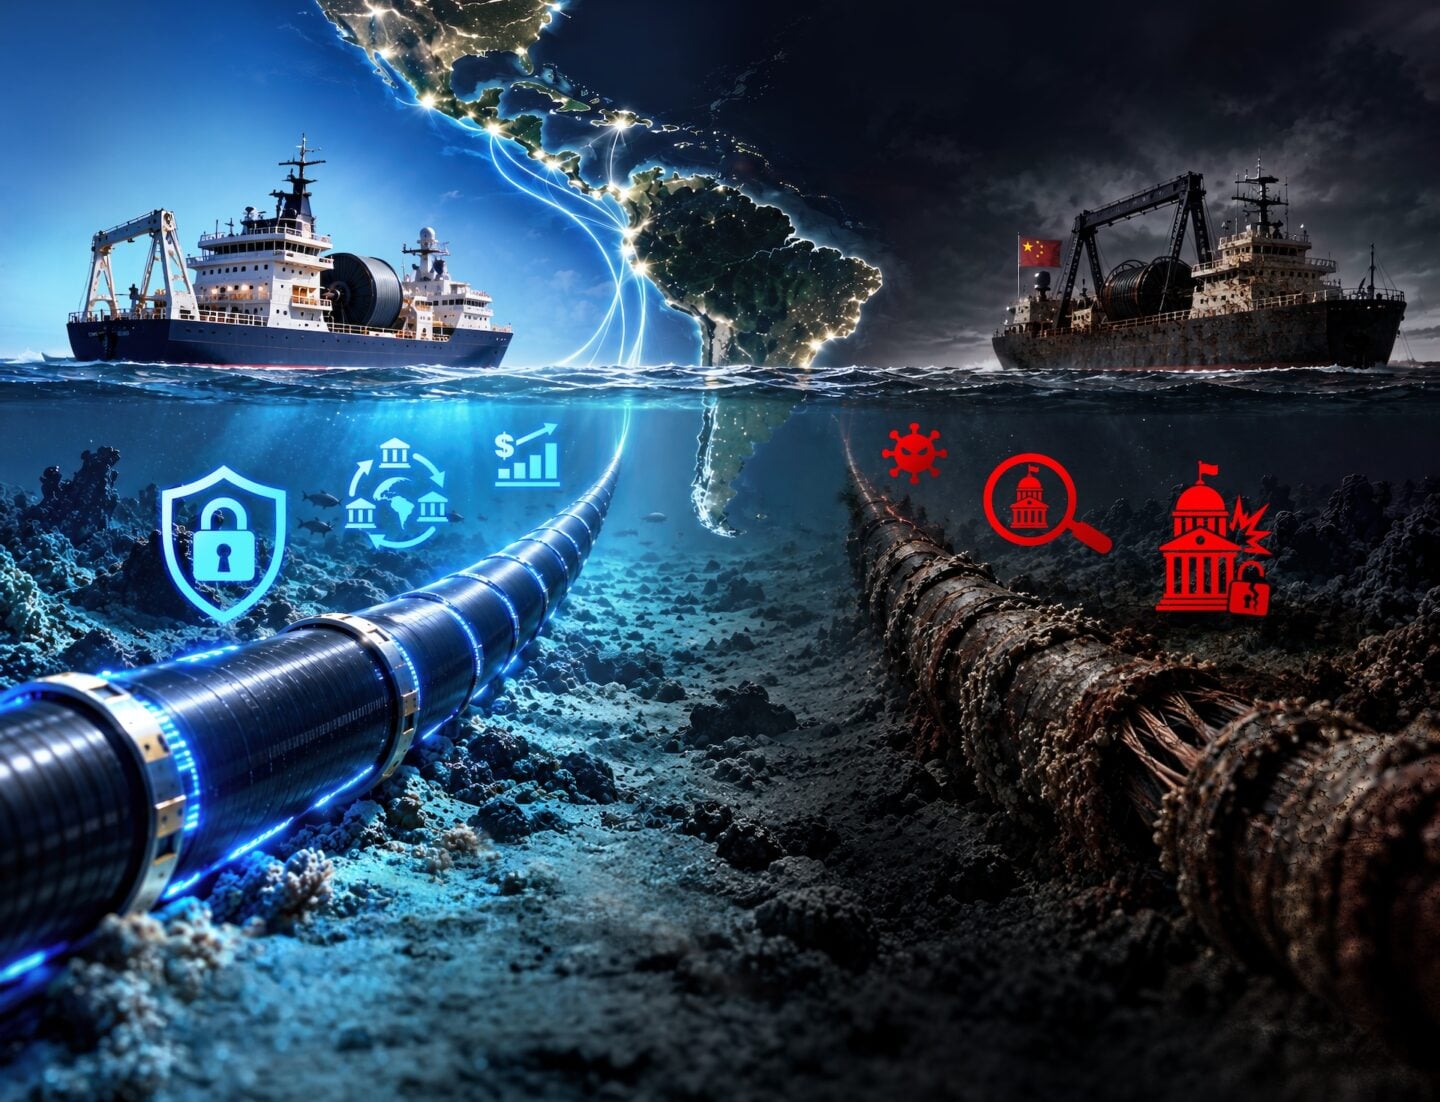
As Chinese companies expand their role in the infrastructure that carries global digital communications, the United States is supporting alternatives for Central America and the Caribbean aimed at reducing dependence on untrusted providers for critical digital infrastructure. Washington plans to allocate nearly $176 million to replace aging telecommunications infrastructure, including undersea cables in Central America and the Caribbean, according to Associated Press. The planned investment would support U.S. and other trusted-provider alternatives amid growing concerns over who builds, supplies, and maintains the networks that carry the region’s digital communications.
“Undersea cables must be considered critical infrastructure for national security. Their importance goes beyond internet connectivity,” Víctor Ruiz, founder of Mexican cybersecurity company SILIKN, told Diálogo. “The impact would be particularly significant in countries that depend on a limited number of cables, landing stations, or concentrated routes, because the loss of a single link could significantly disrupt national and international communications.”
More than 99 percent of international data traffic travels through these networks, according to the International Telecommunication Union (ITU), and communications, financial operations, and digital services depend on them. In July 2026, the ITU’s International Advisory Body for Submarine Cable Resilience and the International Cable Protection Committee (ICPC) warned that geographic concentration, dependence on a limited number of cables, and difficulties carrying out repairs can increase countries’ vulnerability to disruptions. Its recommendations include diversifying routes, strengthening redundancy, and improving coordination between governments and industry.
“Our task now is clear: to turn cooperation into lasting resilience for the infrastructure that keeps the world connected,” said Sandra Maximiano, co-chair of the ITU International Advisory Body, adding that the body’s legacy would be measured by the resilience its recommendations build over the coming decades.
Beijing expands its digital reach
Reuters reported in April 2023 that China Telecom, China Mobile, and China Unicom were developing an approximately $500 million project to connect Asia, the Middle East, and Europe. HMN Technologies, whose predecessor company was majority-owned by Huawei and later came under the control of Hengtong Optic-Electric, would manufacture and install the cable with state subsidies.
That industrial expansion is unfolding alongside China-linked cyberespionage operations. Beijing-sponsored actors have conducted campaigns targeting governments, telecommunications companies, internet service providers, and defense sectors in Latin America and other regions. In 2026, U.S.-based cybersecurity and threat intelligence company Recorded Future identified activity by China-linked groups targeting entities in Mexico, Argentina, and Chile, among other countries in the region. A joint cybersecurity advisory issued in 2025 also warned that these actors compromise telecommunications equipment and networks to maintain long-term access, intercept traffic, and obtain user data, credentials, and network configurations — information that can help Chinese intelligence services track communications and targets in other countries.
“When companies subject to the jurisdiction or influence of the Chinese government are involved, it is critical to assess what level of access, administration, maintenance, or intervention they retain over the infrastructure, as well as the legal obligations and corporate ties that shape their operations,” Ruiz added. “Among the main risks are dependence on second- and third-tier suppliers, a lack of traceability for critical components, privileged access to management systems, software and firmware updates, maintenance credentials, and the possibility of introducing modifications that are difficult to detect.”
Maintenance, a gateway to espionage
The vulnerability lies not only in the cable itself, but also in the systems and companies that manage and repair it. The Wall Street Journal reported in 2024 that U.S. officials had warned telecommunications companies about risks associated with Chinese undersea cable repair ships. The warnings included gaps in the tracking of vessels operated by S.B. Submarine Systems, majority-controlled by China Telecom, raising concerns about the security of commercial and military data traveling through those networks.
“The most sensitive attack surfaces are found in management and monitoring systems, software, firmware, and remote maintenance mechanisms, because these components can provide privileged access without physically compromising the cable,” Ruiz said. “Maintenance is a particularly sensitive point because it requires legitimate access to systems and infrastructure, making it difficult to distinguish authorized activity from malicious action.”
The Caribbean already offers an example of how such risks can influence decisions involving critical infrastructure. In November 2022, the U.S. interagency committee known as Team Telecom recommended rejecting a proposed connection of the ARCOS-1 system to Cuba, citing national security and counterintelligence risks. The U.S. Department of Justice said Cuba’s state-owned ETECSA would have controlled the cable landing station in Cuba and could have gained access to sensitive information traveling through the system. U.S. authorities also expressed concern about the Cuban government’s ties to China and Russia and the possibility that information obtained could be shared with those countries.
Risks to undersea cables also include deliberate physical damage. A Recorded Future report identified nine incidents around Taiwan and in the Baltic Sea during 2024 and 2025. Four involved vessels linked to China or Russia that had opaque ownership structures or carried out suspicious maneuvers near damaged cables.
Trusted providers, secure infrastructure
In comments submitted to the U.S. Federal Communications Commission in August 2026, experts from the Foundation for Defense of Democracies (FDD) warned that undersea infrastructure must be protected not only at the hardware level, but also against persistent access through management systems, service providers, and other trusted relationships. For countries modernizing their networks, this expands the security assessment beyond who manufactures or installs a cable to include who will be able to manage, update, and maintain it throughout its service life.
The New York Joint Statement on the Security and Resilience of Undersea Cables, advanced by the United States in September 2024 and endorsed by the United Kingdom, the European Union, and other countries, establishes principles for protecting this infrastructure. These include selecting secure and trusted providers, ensuring transparency in ownership and operations, preventing damage, strengthening government-industry collaboration, and developing alternative routes.
For Central America and the Caribbean, these decisions have implications that extend beyond a project’s initial cost. In July, A State Department official, speaking to Associated Press on condition of anonymity, said that some Chinese bids may initially appear less expensive but ultimately cost more because of cost overruns, opaque maintenance charges, and performance problems. Dependence on a single provider for installation, operations, and maintenance can also reduce a country’s options over the decades that the infrastructure remains in service.
The choice of providers, therefore, goes beyond commercial considerations and raises questions of operational sovereignty. Contracts that fail to establish adequate controls over components, management systems, updates, and maintenance credentials can create privileged access to infrastructure carrying government, financial, and security communications.
The planned U.S. investment offers countries in Central America and the Caribbean an alternative to greater dependence on China-linked providers for infrastructure that will remain in service for decades. Limiting that dependence, vetting providers, and retaining control over who can access, update, and repair these systems reduces opportunities for potential Chinese access to networks carrying government, financial, and security communications. As the region modernizes its undersea cables, choosing secure infrastructure and trusted providers will also be a strategic decision: preventing Beijing from expanding its influence over systems essential to the security and sovereignty of countries across the region.